London, UK | September 22–24, 2026 | ExCeL London
LogicGate exhibited last week as a Silver Sponsor at the Gartner Security & Risk Management Summit, at ExCeL London, September 22 to 24. At our booth, 2,000+ CISOs and risk leaders saw live demonstrations of Config Newton, LogicGate’s Agentic GRC Engineer, alongside our GRC Agents. One topic dominated the week’s conversations: third-party risk management (TPRM).
As a summit sponsor, we met security and risk leaders from banking, energy, government, pharma, manufacturing, retail, and higher education.
What Did LogicGate Showcase at the Summit?
The centerpiece of our booth was Config Newton, demonstrated live alongside our GRC Agents. Config Newton builds applications on LogicGate’s AI GRC platform from natural-language prompts. Attendees watched it interpret program requirements and build workflows in a live demo.
A human reviews and approves Config Newton’s outputs before and after they are generated, and every action is logged. Practitioners remain the judgment layer. Today, LogicGate’s implementation team uses Config Newton for customer deployments, and an in-platform agent is planned for 2027.
Watching it work in real time hits differently than reading about it. Several demos ended with, “Can we book a proper session after the event?”
And yes, our plush LogicGate goats went quickly. If you managed to grab one (or a Tony’s Chocolonely bar), you know.
Why Was Third-Party Risk Management the Topic of the Week?
Third-party risk management ran through the summit agenda and straight into our booth conversations. In Gartner’s 2026-2027 ThreatScape session, analyst Eric Grenier named software supply chain threats one of four critical threats. We met security leaders managing thousands of suppliers, and teams naming TPRM as the first thing they want to fix.
Vendor ecosystems are simply growing faster than manual, point-in-time assessments can handle.
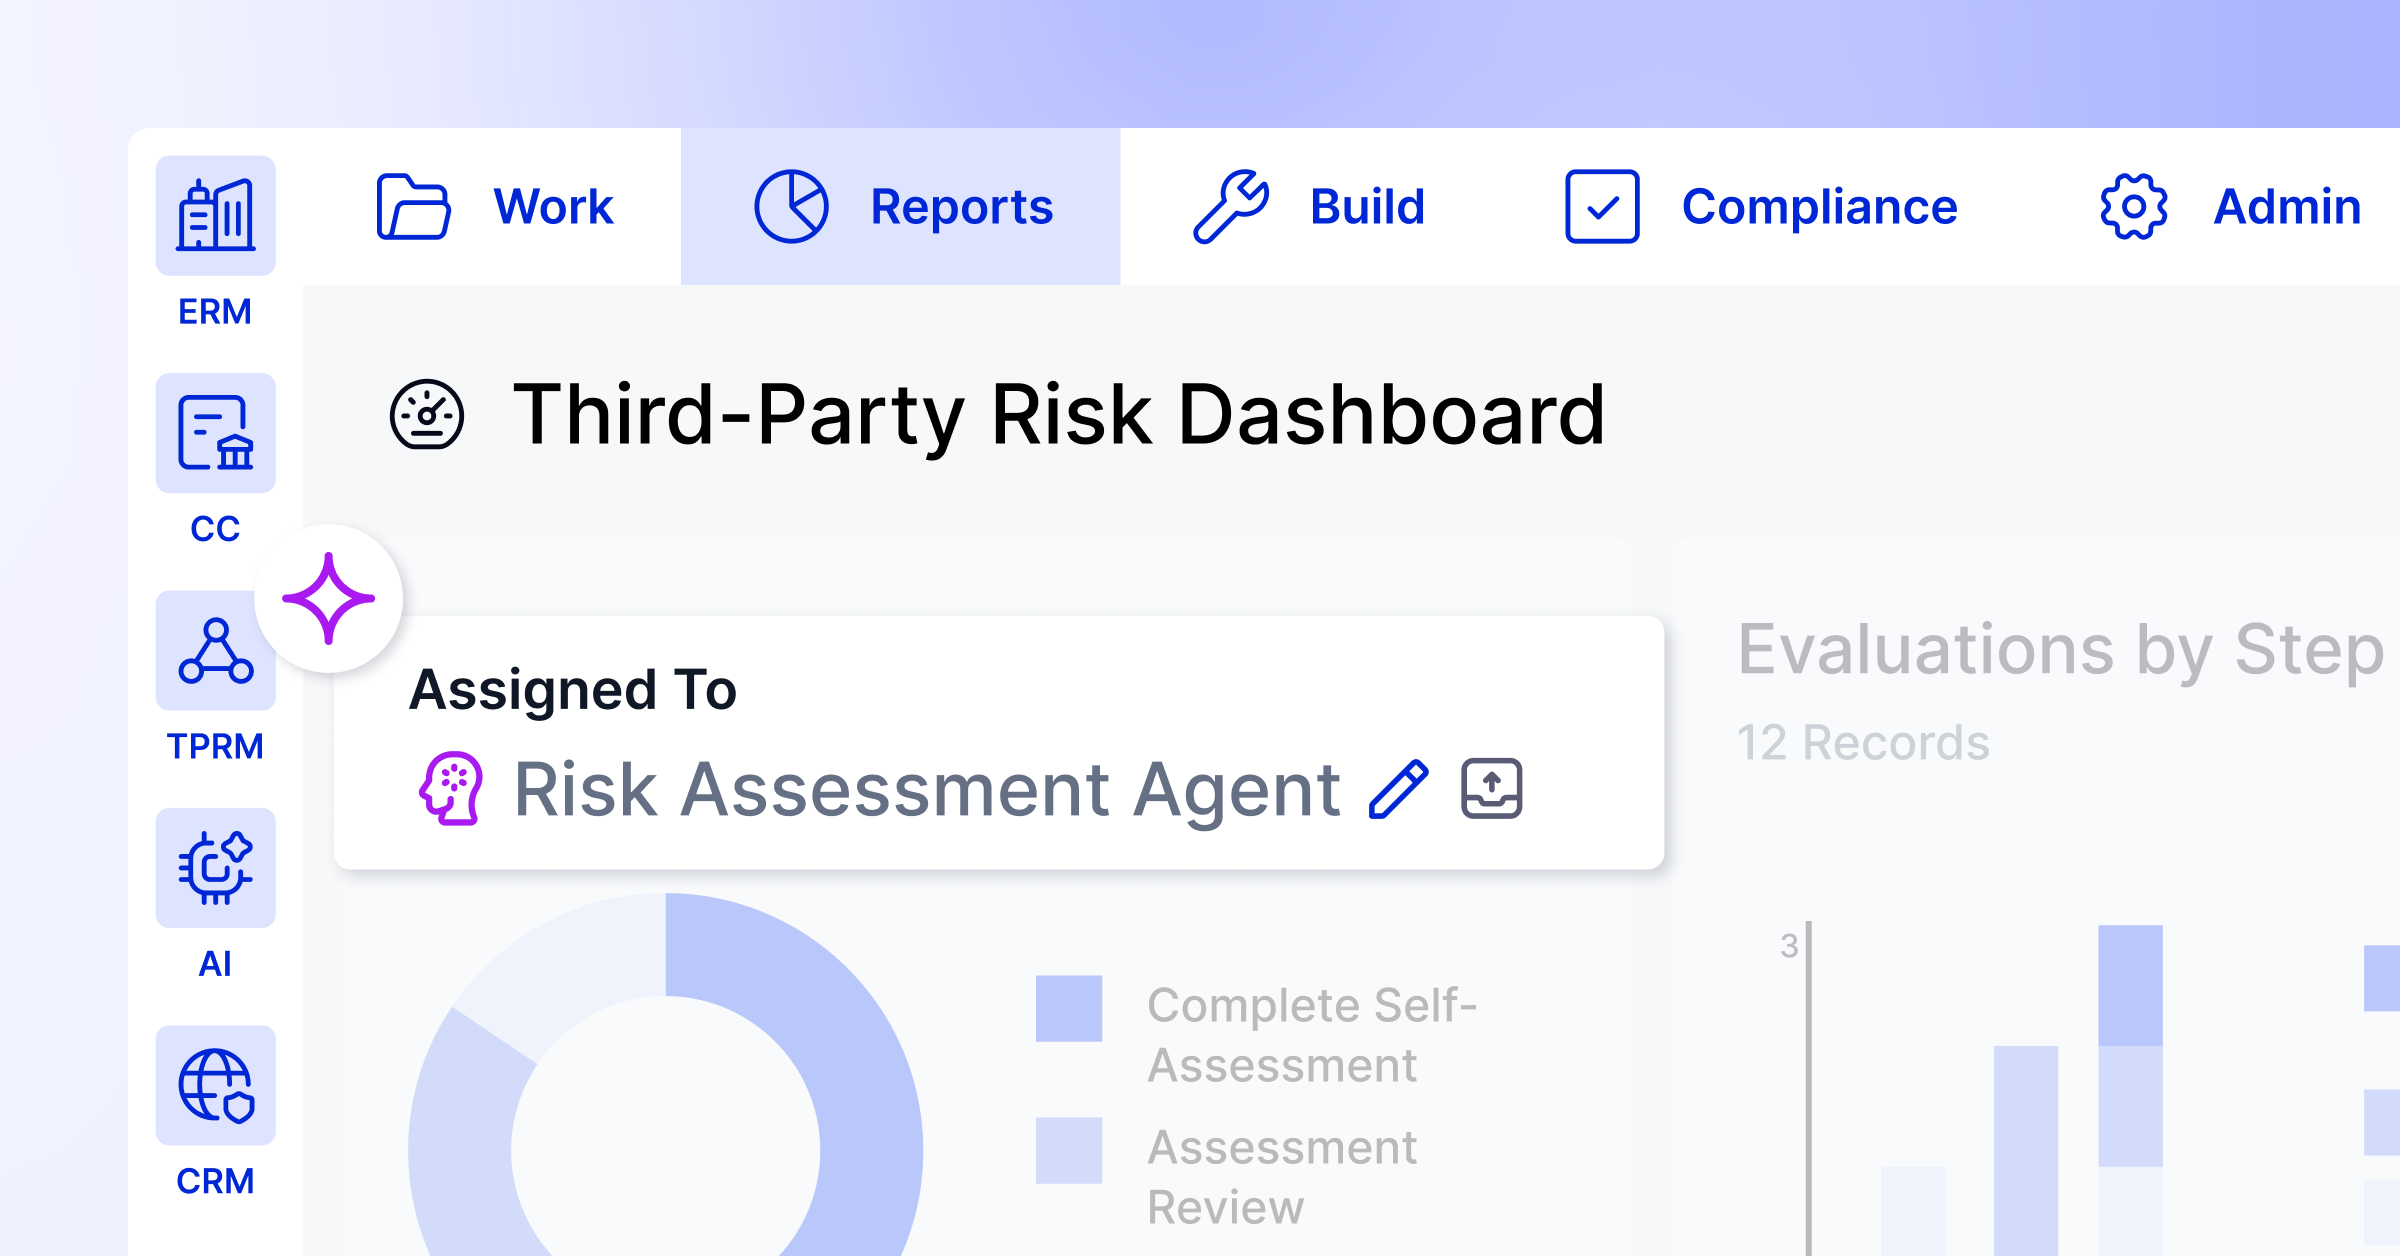
That made our Third-Party Risk Management Agents the most requested demo of the week. Attendees watched them route vendors based on risk signals, complete formal assessments, and flag findings for human-led remediation. Our AI Governance Agents, which triage and score new AI use cases for human review, followed close behind.
GRC Agents are now generally available across TPRM, ERM, AI Governance, and Business Continuity Management. See the Summer 2026 release recap for details.
What Were Security and Risk Leaders Talking About?
The summit’s theme was “Smarter, Faster, Stronger,” and AI dominated the agenda.
Gartner released survey results during the summit. It surveyed 297 CISOs and equivalents from March to May 2026. Forty-one percent reported a social engineering incident involving a deepfake on an employee audio call in the past 12 months.
At the booth, we heard from CISOs, Heads of GRC, IT controls officers, internal audit leaders, and operational risk managers across various industries. A remarkably consistent story emerged:
- The spreadsheet era is ending, painfully. Leader after leader described risk programs that run on Excel, Jira boards, or homegrown low-code apps. No automation, and no single view of risk. As one European finance ministry CISO put it, there are “lots of different areas and a lot of manual work.”
- Point solutions don’t add up to a program. Teams had tried compliance-automation point solutions, only to find they solve audit, third-party risk, and controls in silos. The word we heard over and over: holistic. One healthcare technology CTO overseeing 14 regulatory regions has the program and the people, but needs one platform to run it on.
- Legacy GRC frustration is boiling over. Bank security leaders described incumbent platforms with dozens of modules that are “not agile, not configurable,” with poor reporting.
- Controls compliance is having a moment. “Test once, comply many” came up almost word-for-word from multiple attendees. It came from financial infrastructure leads and public-sector CISOs alike, all juggling overlapping frameworks.
- TPRM and AI governance are the entry points. A manufacturing security leader with 4,000 suppliers. A national rail CISO who wants third-party risk and AI governance before anything else. An internal audit manager expanding beyond audit into both. The pattern repeated constantly.
Where Did the Conversations Continue After the Show Floor?
On Tuesday evening, we co-hosted a happy hour with Risk Rising at the Good Hotel on Royal Victoria Dock. Drinks overlooking the dock led to honest conversation about what’s actually working in European risk programs.
On Wednesday, we hosted an executive dinner in the Gallery Room at Galvin La Chapelle in Spitalfields. No slides, no pitches. Just security and risk leaders comparing notes on AI governance, operational resilience, and elevating GRC’s influence. It was a fitting continuation of the conversations we started at Agility UK in June.
What’s Next?
At Agility 2026, we introduced the Agentic Era of GRC. Gartner Security & Risk London showed strong attendee appetite for agentic, holistic GRC in EMEA.
If we met you at the booth, the happy hour, or over dinner, thank you. If we missed you, speak with our team and see Config Newton and our GRC Agents in action for yourself.
Frequently Asked Questions
Yes. LogicGate was a Silver Sponsor at the summit from September 22–24, 2026 at ExCeL London. We ran live demos of Config Newton and our GRC Agents during the summit.
Config Newton is LogicGate’s Agentic GRC Engineer. It builds applications and workflows on LogicGate’s AI GRC platform from natural-language prompts, with human review and a full audit log on every action.
GRC Agents are generally available now across TPRM, Enterprise Risk Management, AI Governance, and Business Continuity Management. Config Newton is used today by LogicGate’s implementation team, with an in-platform agent planned for 2027.
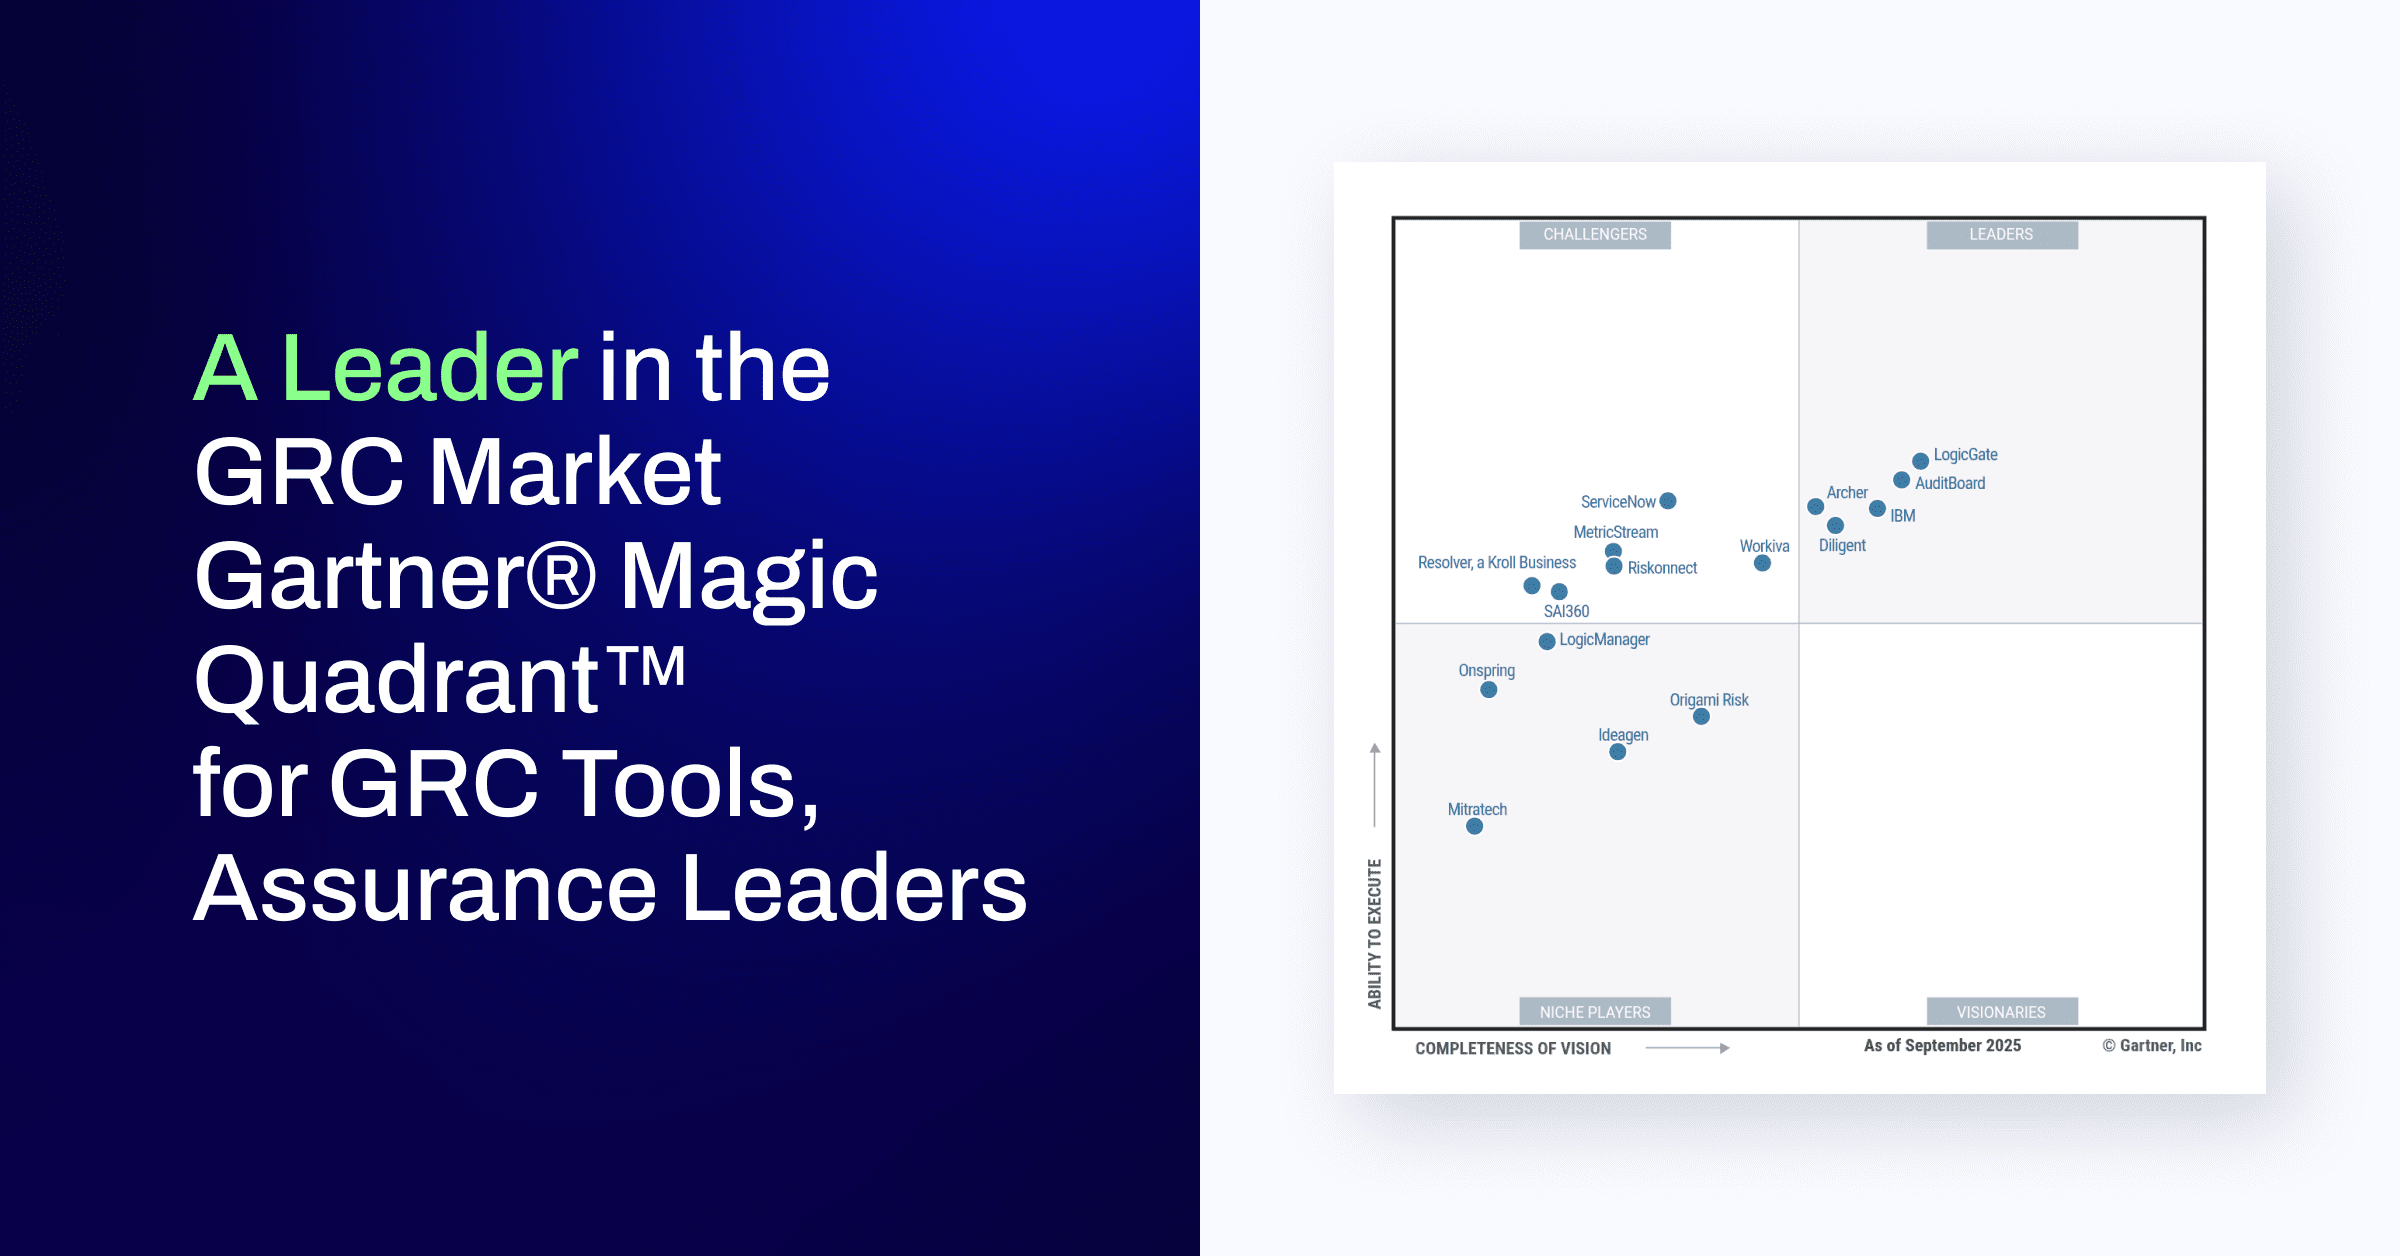
Yes. LogicGate is positioned as a Leader in the Gartner® Magic Quadrant™ for GRC Tools, Assurance Leaders.