TLDR: After two summits with Lowe’s, the takeaways for our team were clear: expressing risk in dollars makes it actionable for the business, and enterprise GRC teams should lean into agentic AI. Lowe’s employees use LogicGate for Code of Ethics certification, and several told us it has simplified, standardized, and automated their daily processes.
Our team spent two back-to-back weeks with our partners at Lowe’s in Charlotte, NC, joining the Third-Party Risk Management (TPRM) Summit on Thursday, October 22, followed by the Lowe’s Information Security Group (ISG) hosted Security Summit on Tuesday, October 27. Here are the highlights.
What Happened at the Lowe’s Third-Party Risk Management Summit?
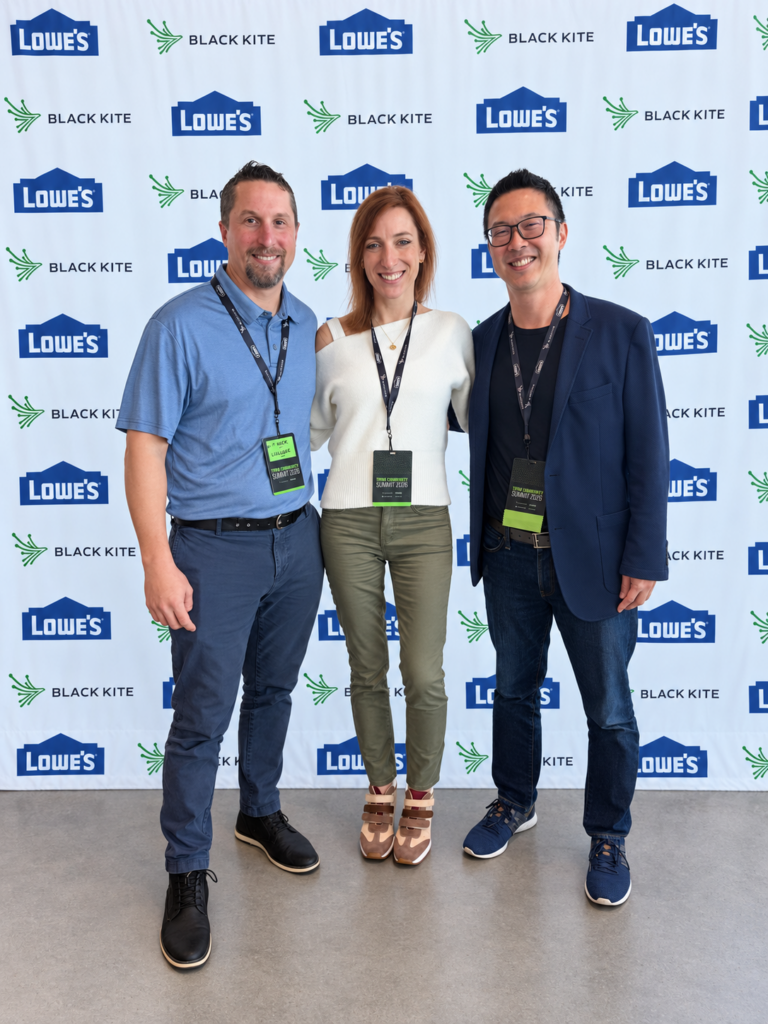
The TPRM Summit was hosted by Lowe’s and co-sponsored by Black Kite and LogicGate. It brought third-party risk practitioners together for a day of practical, forward-looking conversation. Three sessions stood out.
Why Should Risk Be Quantified in Dollars and Cents?
Jack Jones, founder of the FAIR methodology, made the case for risk quantification. His message: financial terms turn risk into a conversation business stakeholders can understand and act on. That is more than a score on a heat map.
What Is the State of TPRM in 2026?
Jefferson Pike, Lowe’s Senior Director of Information Security Governance, Risk, and Compliance, hosted a panel on the challenges and opportunities facing TPRM practitioners this year. It was a candid look at what’s hard about the work today. It also showed where the field has room to grow.Two findings stood out:
- TPRM teams across the industry are struggling with the scale and scope of their responsibilities as they look to intake and assess vendors.
- Automation is no longer a nice-to-have for TPRM teams, it is essential to automate mechanical processes and free up team members to focus on analysis and decision making.
Why Should Enterprise GRC Teams Lean Into Agentic AI?
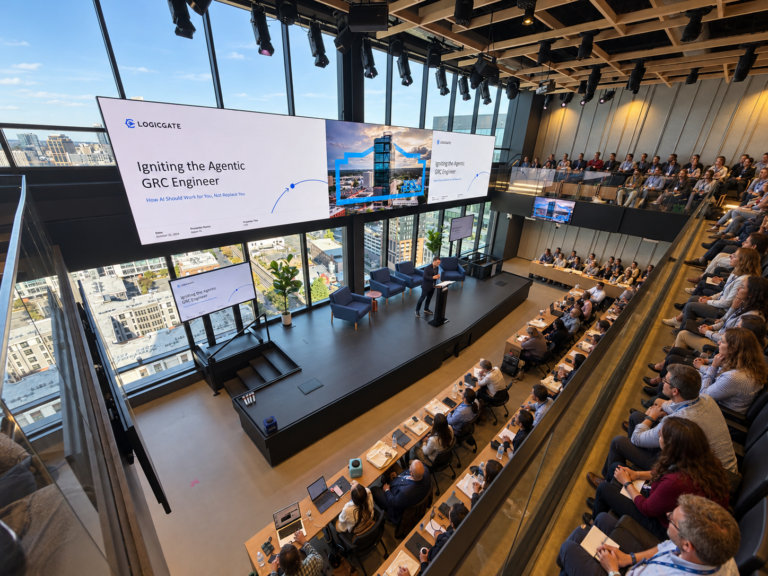
LogicGate’s own CISO, Edwin Ng, spoke on why enterprise GRC teams should lean into agentic AI. His talk was a highlight for our team, and resulted in thoughtful conversations with summit attendees throughout the day.
Our GRC Agents, generally available for TPRM, enterprise risk management, AI governance, and business continuity, keep risk professionals in control of decisions.
What Did We Hear from LogicGate Users at the ISG Security Summit?
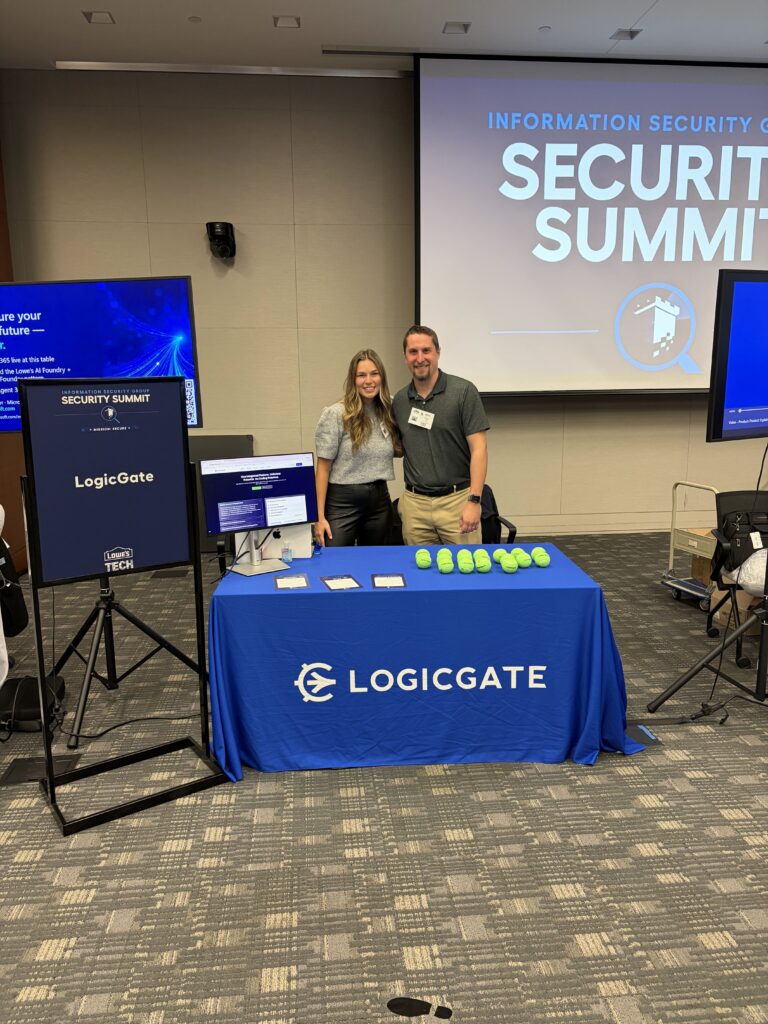
At the ISG Security Summit, Becca Townsend and Matt Meyer met with hundreds of Lowe’s employees to talk about LogicGate. Nearly all of them already knew the platform. Most had used it within the past month to complete their Code of Ethics certification.
The best part was hearing directly from users how LogicGate has made their work lives easier. Several shared that it has simplified, standardized, and automated processes they rely on every day. For a team that builds software to take the friction out of risk and compliance work, there’s no better feedback.
We also enjoyed connecting with our partners on the Lowe’s Information Security Group team. We met many Lowe’s employees who stopped by.
Who Made These Two Summits Possible?
A big thank you to Marc Varner, Chief Information Security Officer at Lowe’s, Jefferson Pike, and the entire ISG team. You put on two spectacular events in back-to-back weeks. We’re grateful for the partnership and can’t wait to keep building together.
Want to see what Lowe’s teams are using? Request a demo today.
Frequently Asked Questions About Lowe’s Summits?
What Was the TPRM Summit?
The TPRM Summit was a day of third-party risk conversation hosted by Lowe’s on Thursday, October 22. Black Kite and LogicGate co-sponsored it. It brought TPRM practitioners together for practical, forward-looking sessions.
Who Spoke at the TPRM Summit?
Jack Jones, founder of the FAIR methodology, spoke on risk quantification. Jefferson Pike of Lowe’s hosted a panel on the state of TPRM in 2026. LogicGate CISO Edwin Ng spoke on agentic AI for enterprise GRC teams.
What Did Jack Jones Say About Risk Quantification?
Jones argued that expressing risk in financial terms makes it a conversation business stakeholders can understand and act on. He contrasted this with a score on a heat map.
How Do Lowe’s Employees Use LogicGate?
Most Lowe’s employees we met at the ISG Security Summit had used LogicGate within the past month. They used it to complete their Code of Ethics certification. Several said it has simplified, standardized, and automated processes they rely on every day.
What Is the ISG Security Summit?
The Lowe’s Information Security Group (ISG) hosted the ISG Security Summit on Tuesday, October 27. Becca Townsend and Matt Meyer of LogicGate met with hundreds of Lowe’s employees there to talk about LogicGate. Nearly all of them already knew the platform.
What Is the FAIR Methodology?
FAIR stands for Factor Analysis of Information Risk. It is a methodology for expressing information and operational risk in financial terms. Jack Jones, who founded FAIR, spoke on risk quantification at the TPRM Summit.
What Is Agentic AI in GRC?
Agentic AI uses AI agents that complete multi-step tasks toward a goal with limited manual input. In GRC, that means agents take on routine work while risk professionals review the output and own the decision. LogicGate CISO Edwin Ng spoke on why enterprise GRC teams should lean into it at the TPRM Summit.